Kempinski data breach hits Switzerland as hackers steal guest bookings
Fraudsters used obtained details to pose as hotel staff and demand payments.
Hackers accessed reservation data from the luxury hotel group Kempinski, and the company says it has since blocked the compromised access.
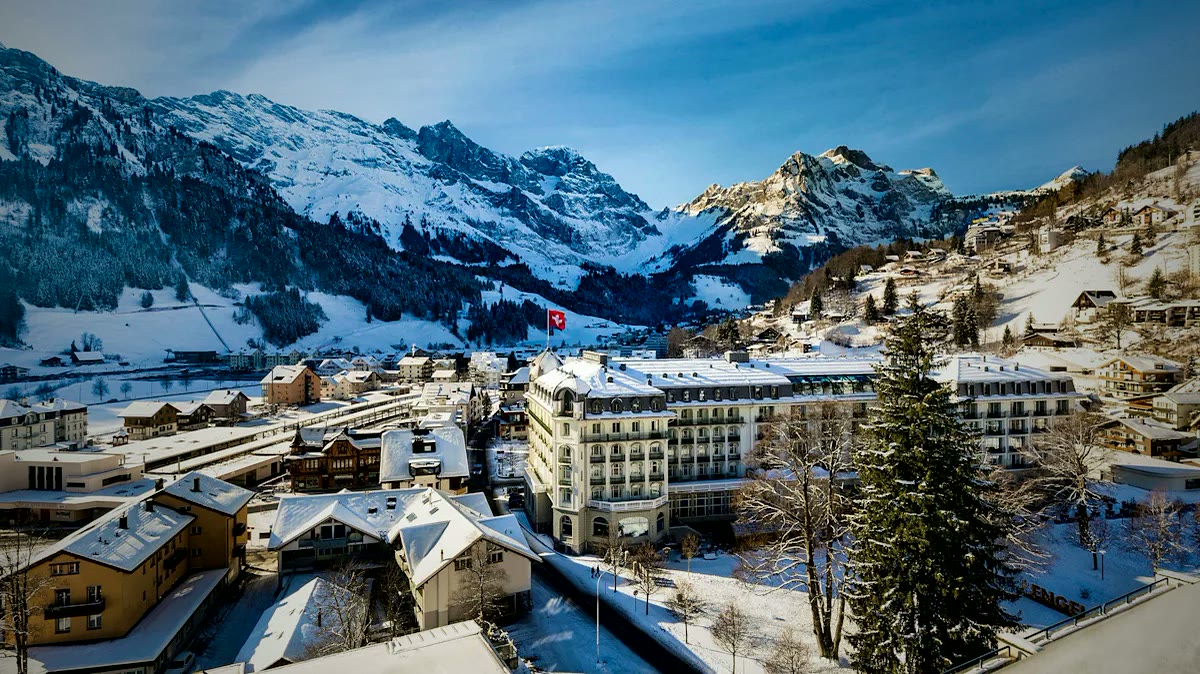
The incident affects guests at Kempinski properties in Switzerland, including the Grand Hotel des Bains Kempinski in St. Moritz and the Kempinski Palace Engelberg. Kempinski says unauthorized access came through the login details of an external technology partner.
After the data was reached, fraudsters allegedly contacted guests using personal information and posed as hotel representatives to demand money. A spokesperson confirmed that the company has already locked the relevant access credentials, shut the access route, and started an investigation with an independent cybersecurity expert.
The hotel group says affected information includes guests’ names, booking details such as hotel name, stay dates and booking number, as well as mobile phone numbers and email addresses. Whether passport or visa numbers were taken could not be confirmed.
Kempinski says payment card details were not affected because such data was not stored in the impacted system. The company has also informed the relevant data protection authorities.
Kempinski warns guests not to follow payment links in suspicious messages, and says it does not ask for payments through links. Guests who may have shared payment information with the fraudsters should contact their bank to block the affected card and report the matter to police.
At the latest, Kempinski says it is working with the affected technology partner to better secure its infrastructure, while the investigation is ongoing.
ADVERTISEMENT
Source:
20 Minuten